S4Core Core Infrastructure for the Digital Edge

S4Core

Core Infrastructure for the Digital Edge

Latest Articles

Whoever Owns the Nameservers Owns the Business
Infrastructure & Operations

Whoever Owns the Nameservers Owns the Business

Architecture diagrams start at the load balancer; reality starts at the resolver. Registrar locks, inherited TTLs, half-finished DNSSEC rollovers, and nameserver dependencies form a control plane most teams neither own nor monitor — until a routine provider change turns into a total outage.
Your Edge Region Is Not Your Customer's Front Door
Architecture & Strategy

Your Edge Region Is Not Your Customer's Front Door

Region-to-region benchmarks measure the part of the network you control. For most US users, latency is decided in the last mile — by ISP peering, mobile carriers, home gateways, and device variability. A latency budget that stops at the edge map is a budget for the wrong trip.

A Green Backup Dashboard Proves Nothing Without a Restore Record
Resilience & Recovery

A Green Backup Dashboard Proves Nothing Without a Restore Record

Backup jobs report success; recovery reports failures nobody has read. The distance between a scheduled snapshot and a proven restore path is where real RTO lives, and it is closed only by recurring drills with measurable pass or fail outcomes.

The Abstraction Trap: How Modern Infrastructure Platforms Engineer Their Own Indispensability
Architecture & Strategy

The Abstraction Trap: How Modern Infrastructure Platforms Engineer Their Own Indispensability

Vendor lock-in has evolved. It no longer arrives through explicit proprietary formats or obvious contractual constraints—it arrives through layers of elegant abstraction that make deep coupling feel like architectural sophistication. By the time most teams recognize the dependency they have built, the cost of reversing it has become indistinguishable from the cost of a complete platform rebuild.

What the Logs Never Captured: Infrastructure Failures That Exist Outside Your Observability Stack
Infrastructure & Operations

What the Logs Never Captured: Infrastructure Failures That Exist Outside Your Observability Stack

The most dangerous infrastructure failures are not the ones that generate alerts—they are the ones that generate nothing at all. Modern observability architectures are sophisticated, expensive, and instrumented at extraordinary depth, yet entire categories of failure exist entirely outside their detection range. Understanding what those categories are, and why they escape notice, is a prerequisite for building infrastructure that can actually be trusted.

Fossilized Knowledge: The Silent Drift Between Infrastructure Documentation and Reality
Architecture & Strategy

Fossilized Knowledge: The Silent Drift Between Infrastructure Documentation and Reality

Infrastructure documentation decays quietly and continuously, long before anyone notices the gap between what teams believe their systems do and what those systems actually execute at runtime. The problem is not negligence—it is structural. As infrastructure evolves at the speed of deployment pipelines, documentation evolves at the speed of human attention, and those two velocities are rarely compatible.

The Local Development Lie: How Developer Convenience Is Quietly Undermining Production Stability
Infrastructure & Operations

The Local Development Lie: How Developer Convenience Is Quietly Undermining Production Stability

Infrastructure decisions made in the name of developer velocity rarely stay confined to local environments. This article examines how patterns optimized for fast iteration — loose validation, minimal resource constraints, and environment-specific shortcuts — accumulate into production liabilities that surface at the worst possible moments.

Orchestration Overhead: When Kubernetes Becomes the Problem It Was Meant to Solve
Architecture & Strategy

Orchestration Overhead: When Kubernetes Becomes the Problem It Was Meant to Solve

Kubernetes promised to abstract away infrastructure complexity, but for many organizations it has quietly become the most demanding system in their stack. This article examines the structural gap between what container orchestration offers in theory and what it extracts in operational cost, and asks whether teams are honest with themselves about the scale at which Kubernetes actually pays off.

Counting Copies, Ignoring Causes: The False Confidence of Numerical Redundancy
Architecture & Strategy

Counting Copies, Ignoring Causes: The False Confidence of Numerical Redundancy

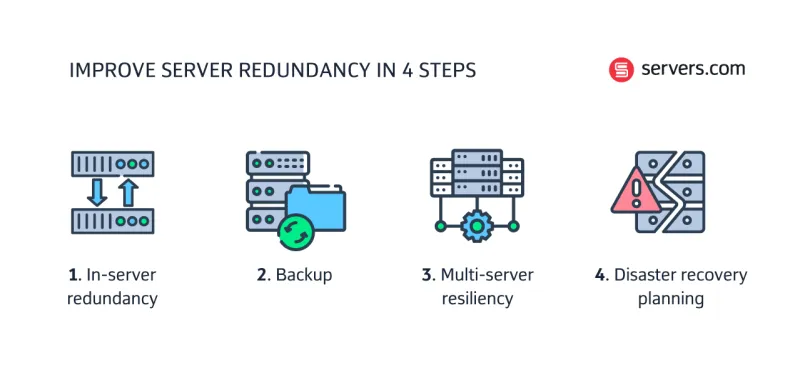
Running three instances of a service across two availability zones looks like resilience on paper. When those instances share a database, a certificate authority, or a misconfigured security group, the redundancy is largely cosmetic. This article examines why true fault tolerance demands architectural diversity rather than duplicated components that fail together.

State Everywhere: The Uncomfortable Truth About What Your Stateless Architecture Is Actually Managing
Architecture & Strategy

State Everywhere: The Uncomfortable Truth About What Your Stateless Architecture Is Actually Managing

Stateless architecture has become one of distributed systems design's most durable articles of faith—a design principle so widely adopted that questioning it feels almost heretical. Yet the systems built under this banner routinely accumulate state in caches, queues, edge layers, and external stores, creating complexity that rivals the monoliths they replaced. This piece challenges the premise and offers a more honest accounting of what modern distributed systems are actually managing.

High Availability on Paper: How Load Balancing Configurations Manufacture Confidence While Hiding Decay
Infrastructure & Operations

High Availability on Paper: How Load Balancing Configurations Manufacture Confidence While Hiding Decay

Load balancers are the infrastructure industry's most trusted confidence builders—and one of its most reliable sources of false assurance. When traffic distribution dashboards report clean, even splits across healthy nodes, the underlying reality is often far more complicated. This piece examines how standard load balancing configurations mask systemic degradation until the moment they cannot.

The Invisible Attack Surface: Transitive Dependencies and the Supply Chain Vulnerabilities Container Scanners Cannot Reach
Architecture & Strategy

The Invisible Attack Surface: Transitive Dependencies and the Supply Chain Vulnerabilities Container Scanners Cannot Reach

Container image scanning has become a standard fixture in modern CI/CD pipelines, providing teams with a defensible checkpoint against known vulnerabilities. But the security model it enforces covers only the outermost layer of a dependency graph that can run dozens of levels deep. This article examines how transitive supply chain attacks exploit precisely the blind spots that scanner-first security strategies leave unaddressed.

Healing Itself to Death: The Architectural Blind Spots Created by Auto-Remediation
Architecture & Strategy

Healing Itself to Death: The Architectural Blind Spots Created by Auto-Remediation

Automated self-healing mechanisms promise resilience but frequently deliver something more dangerous: systems that conceal their own structural failures. When rollbacks fire automatically, when auto-scaling absorbs load spikes without human review, and when self-healing loops resolve symptoms without addressing causes, the underlying architecture quietly deteriorates. The case for defensive automation — systems that alert before they act — has never been more urgent.

The Polyglot Tax: What Heterogeneous Infrastructure Actually Costs at Scale
Architecture & Strategy

The Polyglot Tax: What Heterogeneous Infrastructure Actually Costs at Scale

The polyglot cloud movement has made supporting multiple languages, runtimes, and deployment patterns a marker of engineering sophistication. But for organizations operating at scale, this heterogeneity carries a compounding operational cost that rarely appears in initial architectural decisions. From institutional knowledge fragmentation to debugging complexity, the case for infrastructure diversity deserves a more rigorous accounting.

Drowning in Clarity: How Metric Overload Is Quietly Destroying Your Debugging Capability
Infrastructure & Operations

Drowning in Clarity: How Metric Overload Is Quietly Destroying Your Debugging Capability

Teams that instrument every conceivable system behavior often find themselves less capable of diagnosing failures than those operating with disciplined, minimal monitoring. The paradox is real: more metrics can produce worse outcomes. Understanding why requires a hard look at cognitive load, alert fatigue, and the difference between data collection and operational intelligence.

One Size Fits None: The Hidden Failures of Infrastructure Monoculture
Architecture & Strategy

One Size Fits None: The Hidden Failures of Infrastructure Monoculture

The pursuit of infrastructure standardization promises operational simplicity, but organizations that enforce uniformity across every team and workload often discover a harder truth: rigid systems fracture under pressure. When edge cases, performance anomalies, and business-critical demands arrive—and they always do—monocultures have no flex left to give.

The Infrastructure You Forgot You Were Running: Confronting the True Cost of Dormant Systems
Infrastructure & Operations

The Infrastructure You Forgot You Were Running: Confronting the True Cost of Dormant Systems

Across enterprise cloud environments, a quiet accumulation of dormant components—deprecated microservices still consuming compute, orphaned storage volumes, outdated routing rules, and over-provisioned capacity that was never reclaimed—drains budgets and complicates incident response in ways that rarely surface until a crisis forces the issue. Addressing this infrastructure cruft requires more than tooling; it requires confronting the organizational inertia that lets it grow.

The Millisecond Toll: How Security-First Architecture Accumulates a Performance Debt You Can't Ignore
Infrastructure & Operations

The Millisecond Toll: How Security-First Architecture Accumulates a Performance Debt You Can't Ignore

Modern security architecture—mutual TLS, zero-trust enforcement, identity verification at every service boundary—is essential infrastructure. But each layer of protection carries a latency cost, and in distributed systems those costs compound in ways most teams never measure. Understanding and optimizing the performance overhead of security controls is not optional; it is a core infrastructure responsibility.

When Partial Becomes Total: The Engineering Failure of Modern Graceful Degradation
Infrastructure & Operations

When Partial Becomes Total: The Engineering Failure of Modern Graceful Degradation

The ability to serve degraded but functional responses during partial outages was once a foundational expectation of resilient system design. Today, the same automation and interconnection that makes distributed infrastructure powerful has systematically eroded that capability. This article examines the architectural patterns driving catastrophic failure under partial load conditions and proposes concrete approaches for restoring predictable behavior when things go partially wrong.

Secrets Without a Paper Trail: Closing the Audit Gap in Credential Lifecycle Management
Architecture & Strategy

Secrets Without a Paper Trail: Closing the Audit Gap in Credential Lifecycle Management

Most organizations have invested in secrets management tooling, but far fewer have built the audit infrastructure needed to answer a fundamental forensic question: what happened to this credential, and when? The gap between compliance-driven rotation policies and genuine credential hygiene is wider than most security teams realize, and it carries significant consequences for breach investigation, regulatory accountability, and operational continuity across hybrid environments.